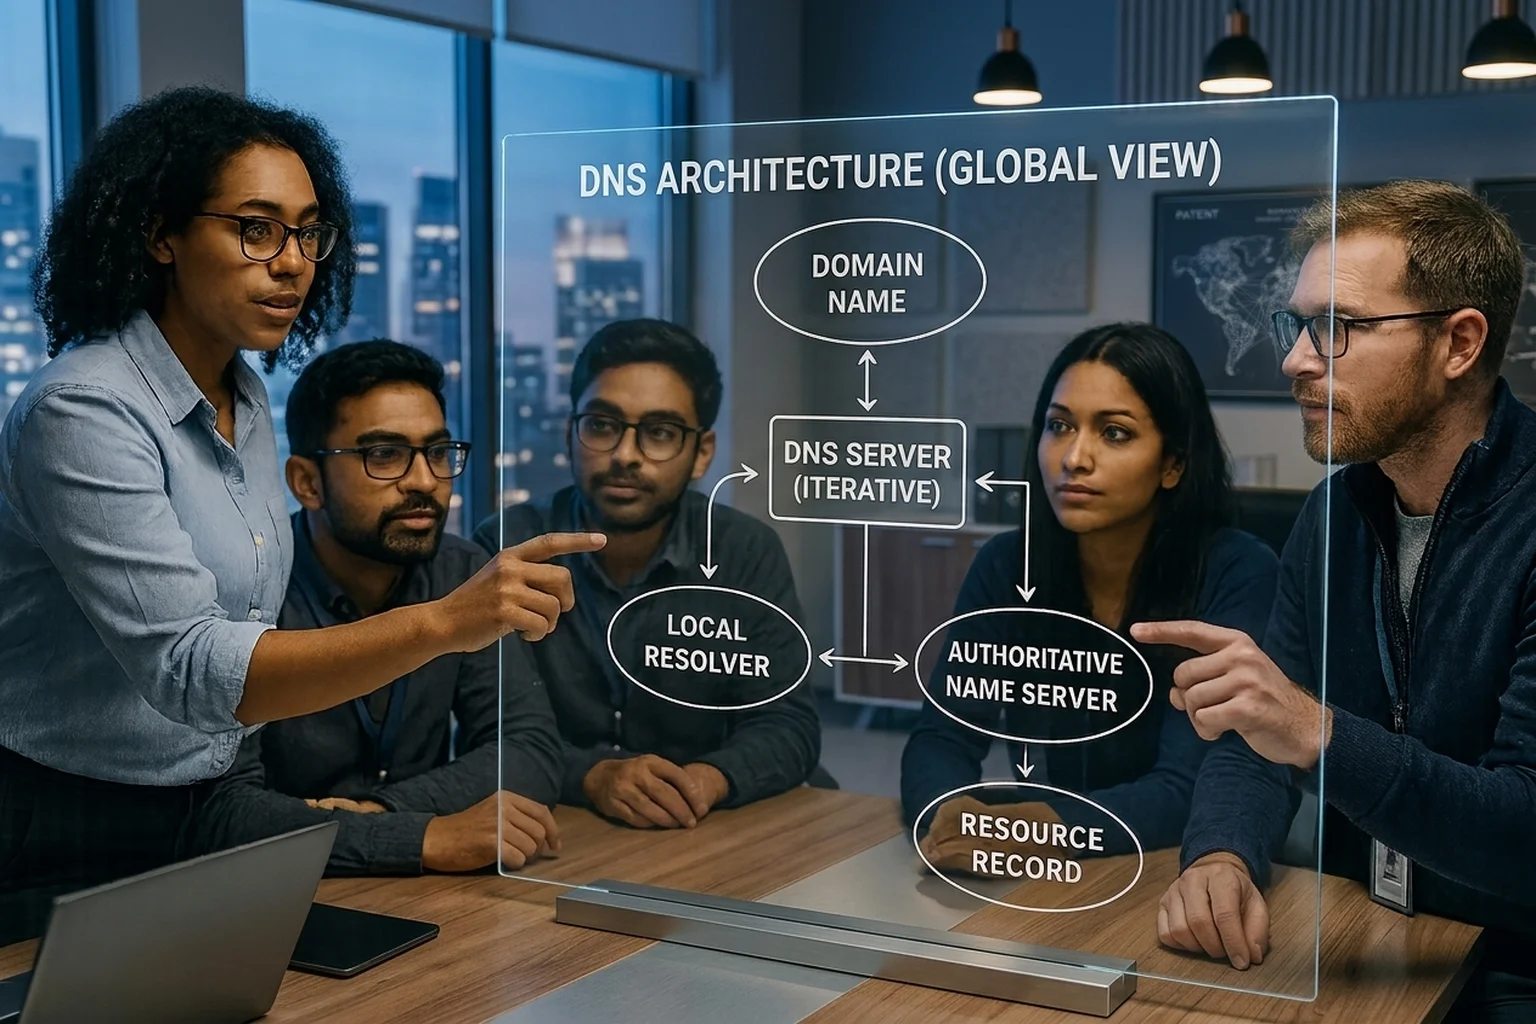
Comprehensive guide to authoritative master DNS, local resolvers, diagnostic commands, and DNS records.
Master DNS & Local Resolvers
How DNS Works Globally
The Domain Name System (DNS) functions as the global directory of the Internet. It translates human-readable domain names (such as www.example.com) into numerical IP addresses (such as 192.168.1.1) that networked computers use to route packets. This translation layer is fundamental because humans remember names far more easily than numeric sequences.
DNS query for www.example.com
Queries upstream DNS servers
Supplies authoritative response
IP address returned to client
This hierarchical architecture enables fast and scalable domain name resolution while distributing traffic across thousands of authoritative servers worldwide.
Master DNS: Authoritative Name Servers
Master DNS servers, also known as authoritative nameservers, hold the definitive source records for a specific domain. They represent the ultimate source of truth for all DNS resource records within their assigned zone.
Every domain maintains at least two master DNS servers storing authoritative information:
- DNS Zone: Database containing all domain resource records
- Zone File: Structured configuration file containing records
- Resource Records: A, AAAA, MX, CNAME, TXT, SOA, etc.
When a recursive resolver queries a master server, the server answers authoritatively from its local zone database.
Key Architectural Differences
| Function | Master DNS | DNS Resolver |
|---|---|---|
| Primary Role | Authoritative source of DNS records | Queries upstream and caches responses |
| Scope | Specific assigned domain(s) | Resolves all domains via recursive lookup |
| Management | Domain owners / Registrars | End users or internet service providers |
| Updates | Manual or automated via API | Dynamic via cache expiration (TTL) |
| Security | DNSSEC signing, access control lists | DoH/DoT transport encryption, local filtering |
Master DNS servers are typically managed by domain registrars or system administrators. Industry-standard software packages include BIND, PowerDNS, and NSD.
Types of DNS Records
DNS records are the foundational data units maintained in zone files on authoritative master servers. Here are the core record types every administrator should know:
| Record Type | Description |
|---|---|
| A Record | Maps a hostname to an IPv4 address |
| AAAA Record | Maps a hostname to an IPv6 address |
| PTR Record | Used for reverse DNS resolution (IP address to hostname) |
| CNAME Record | Creates a canonical alias pointing to another domain name |
| MX Record | Specifies mail exchange servers responsible for the domain |
| NS Record | Identifies the authoritative nameservers for a zone |
| SOA Record | Contains administrative metadata about a DNS zone |
| SRV Record | Specifies hostnames and port numbers for specific services |
| TXT Record | Stores arbitrary text data (SPF, DKIM, site verification) |
| CAA Record | Specifies which Certificate Authorities may issue TLS certificates |
| DNSKEY Record | Contains public keys used in DNSSEC chain-of-trust verification |
These records are essential for configuring a domain correctly and ensuring seamless interoperability across the Internet.
Local DNS Resolvers
Local DNS resolvers are DNS servers deployed directly within a local network or on an individual endpoint. Their primary mission is handling outbound client requests, querying upstream servers, and caching answers locally to maximize speed and privacy.
Client sends lookup request to the local resolver
Resolver checks its high-speed local memory cache first
If not cached, it iteratively queries the DNS hierarchy
Validates cryptographic signatures (RRSIG) to detect tampering in transit
Applies blocking rules and security policies (e.g. Unbound local-zone)
Delivers the validated answer back to the requesting client
Stores the response in cache for subsequent requests according to TTL
Local resolvers deliver substantial technical advantages:
- Privacy: DNS queries remain strictly inside your local perimeter
- Performance: Sub-millisecond latency for repeated lookups from cache
- Security: Proactive blocking of malicious domains and trackers
- Control: Granular customization of local resolution policies
- Independence: Freedom from ISP DNS logging and tampering
Unbound: The Premier Local Recursive Resolver
Unbound is an open-source, lightweight, validating recursive DNS resolver developed by NLnet Labs. Engineered for high performance and security, it has become the standard choice for home labs, privacy enthusiasts, and enterprise edge networks.
Unbound
Local recursive validating resolver
Root DNS Servers
Global starting point for domain discovery
TLD Servers
Authoritative operators for .com, .org, etc.
Master DNS
Authoritative nameservers for the target domain
Unbound stands out through its advanced architectural features:
- DNSSEC Validation: Native cryptographic verification of trust chains
- Optimized Caching: Prefetching popular entries before expiration
- Transport Encryption: Native support for DNS over TLS (DoT) and DoH
- Lightweight Footprint: Minimal memory and CPU consumption in C
- Hardened Security: Robust defense against cache poisoning attacks
Unlike forwarding proxies, Unbound performs full iterative recursion independently.
Relationship Between Master DNS and Local Resolvers
The relationship between authoritative master servers and local recursive resolvers like Unbound forms the backbone of Internet navigation. Here is how they interact:
Master DNS
Authoritative server holding definitive source records for a zone
Local Resolver (Unbound)
Queries master nameservers directly and caches responses
Client
Requests domain name resolution for applications
Resolution Workflow
Client Query
Client requests resolution for a hostname
Cache Inspection
Unbound prioritizes local memory cache lookup
Discovery
Identifies authoritative master servers for the zone
Direct Query
Unbound queries the authoritative master directly
Authoritative Reply
Master nameservers return official zone records
Cache & Delivery
Answer is cached in RAM and delivered to the client
Direct interaction between recursive resolvers and authoritative masters ensures high data freshness, native DNSSEC verification, elimination of intermediate aggregators, and maximum query privacy.
Role of ISP DNS in the Ecosystem
ISP DNS servers are recursive resolvers operated by internet service providers. While convenient out of the box, their operational characteristics differ markedly from a dedicated local resolver like Unbound.
ISP DNS Operations
Performs upstream recursive lookups across the hierarchy
Caches responses across millions of provider subscribers
Enforces carrier filtering, redirection, and logging policies
Key Differences
| Feature | Local Resolver (Unbound) | ISP DNS |
|---|---|---|
| Location | Running locally on your network or host | Hosted in ISP data centers |
| Control | Total — you define rules, overrides, and caching behavior | None — ISP dictates policies and filtering |
| Privacy | Queries stay local; external lookups are direct or encrypted | Every lookup is logged and tied to your IP |
| Performance | Sub-millisecond RAM cache responses | Subject to WAN connection latency and load |
| Security | Full DNSSEC validation with zero tampering | DNSSEC support varies; risk of NXDOMAIN hijacking |
DNS Interaction Architecture
A visual breakdown of how traffic flows between clients, local resolvers, and global infrastructure:
Local Client
Web Browser, Operating System, Applications
Local Resolver
Unbound, dnsmasq, Pi-hole
External DNS Infrastructure
Root Servers, TLD Nameservers, Master DNS
Resolution Pipeline Breakdown
Query Dispatch
Client sends lookup request to Unbound
Cache Inspection
Unbound checks local memory cache immediately
Root & Upstream Recursion
Iterative queries to root and TLD nameservers
Authoritative Reply
Master DNS responds with official zone data
Validation & Delivery
DNSSEC validated, cached in RAM, returned to client
Benefits of Local Resolvers Like Unbound
Deploying a dedicated local resolver delivers substantial advantages over relying on external public resolvers or default ISP settings:
By running Unbound, you regain sovereignty over your DNS traffic, mitigate exposure to external surveillance, and optimize network responsiveness.
Did You Know?
Explore these essential DNS concepts to master DNS architecture and optimize your local resolver configuration:
Advanced DNS Security
Securing the transport and validation layer between clients, local resolvers, and master DNS servers is critical for defeating modern network attacks:
Common Threats
Security Defenses
DNSSEC Validation Workflow
DNSSEC (Domain Name System Security Extensions) introduces cryptographic authentication to DNS. By attaching verifiable digital signatures to resource records, it guarantees that lookup answers originate from the legitimate zone owner and have not been altered in flight.
1. Data Signing
The domain owner signs resource records with a private Zone Signing Key (ZSK).
2. Key Publication
Public keys are published as DNSKEY records and authenticated via parent DS records.
3. Chain of Trust
Resolvers validate signatures iteratively from the root trust anchor down to the child zone.
4. Final Verification
The resolver checks the cryptographic signature before delivering the response to the client.
Essential DNS Diagnostic Commands
These practical CLI commands empower administrators to diagnose resolution latency, examine zone records, and verify DNSSEC validation. Click the copy button to copy any command to your clipboard:
DNS Quiz
Test your knowledge of master DNS, local resolvers, and DNSSEC with this interactive quiz. Click on any card to reveal the answer!
You have completed the quiz! How many correct answers did you get?
Conclusion
This guide examined the complementary roles of authoritative master DNS and local recursive resolvers like Unbound within the global Internet architecture. Understanding how these layers communicate is essential for designing resilient, high-speed, and secure network infrastructure.
Deploying a local validating resolver like Unbound represents one of the most effective steps you can take to safeguard personal and organizational privacy. By taking ownership of your DNS pipeline, you eliminate reliance on third-party aggregators, stop telemetry harvesting, and guarantee cryptographic authenticity for every lookup.
📚 openSUSE Unbound Guide
Official documentation and step-by-step tutorial for deploying, configuring, and hardening Unbound on openSUSE systems.
⚙️ 15 Essential Options
Comprehensive breakdown of critical Unbound directives for optimizing cache performance, enforcing strict DNSSEC, and preventing query leakage.
💻 Unbound Configuration on GitHub
Production-ready Unbound configuration templates, anti-tracking filtering lists, and security hardening scripts tested in production.
By mastering the concepts covered in this guide and leveraging command-line diagnostic tools, you are well-equipped to troubleshoot resolution anomalies, protect your infrastructure, and optimize network throughput.
👥 Comments
Comment on this article